

Executive Overview
In an era where healthcare administration relies heavily on digital record-keeping systems, the integrity of computer databases is foundational to business operations and patient trust. However, the vulnerabilities inherent in internal data management systems were recently laid bare at a local eye care clinic in Evansville, Indiana.
What began as a routine internal audit concerning a minor financial discrepancy quickly escalated into a complex criminal investigation involving corporate fraud, identity manipulation, and digital sabotage.
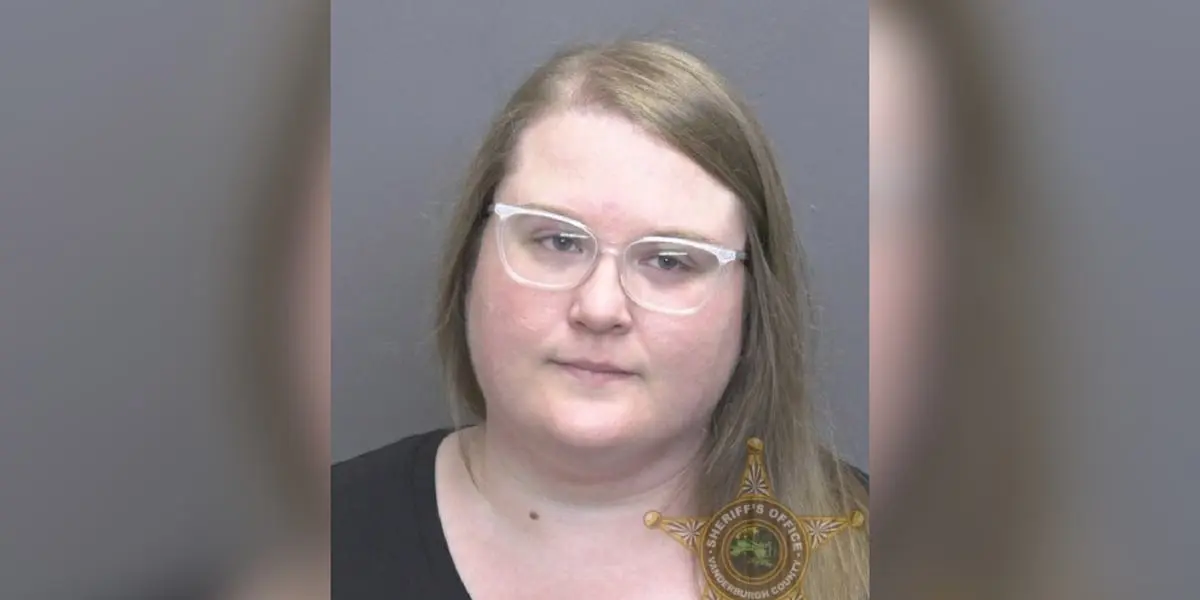
Law enforcement officials with the Evansville Police Department (EPD) arrested 35-year-old Hannah Richardson following a detailed fraud report filed by the management of the Brizius, Embry & Smith optometry office.
According to investigators, Richardson—a former employee at the clinic—embarked on a calculated campaign to erase her own personal financial obligations to the practice.
However, what started as an apparent self-serving maneuver to delete an $80 personal billing ledger unraveled into a much larger digital catastrophe.
Investigators and internal IT specialists discovered that over a span of less than two weeks, Richardson had allegedly altered hundreds of patient files, tampered with insurance adjustments, compromised financial accounts, and utilized a coworker’s credentials without authorization.
The scope of the alleged sabotage extended far beyond simple bookkeeping errors. Cybersecurity and forensic evaluations indicate that the modifications were designed not only to defraud the optometry practice of tens of thousands of dollars but potentially to throw the clinic’s financial administrative systems into complete chaos.
If the unauthorized alterations had gone unnoticed, the clinic faced potential direct financial losses exceeding $25,000, while numerous innocent patients could have faced improper re-billing for services and products they had already fully settled.
Richardson now faces multiple serious felony charges, including theft, fraud, and the unlawful modification of computer data.
This case serves as a striking reminder of the insider threats facing modern medical practices, highlighting the critical need for strict digital access controls, robust audit trails, and multi-layered cybersecurity protocols within small and medium-sized healthcare environments.
Detailed Chronology of Events
The Genesis of the Investigation: June 22 – July 2
The timeline of the alleged digital tampering centers on a brief yet destructive ten-day window during the summer. According to police reports and investigative findings compiled by the Evansville Police Department, the unauthorized modifications to the Brizius, Embry & Smith computer database occurred between June 22 and July 2.
During this period, Richardson was still actively employed by the optometry office, granting her routine access to the internal network and practice management software.
For management and clinic owners, these days initially appeared to be standard business operating periods. Employees processed appointments, billed insurance providers, and logged patient payments as usual.
Yet, beneath the surface, the office’s database was being systematically altered. Crucial ledgers detailing outstanding balances, insurance reimbursements, and patient-rendered payments were being modified, overwritten, or deleted entirely.
The Resignation and Discovery
On July 2, Richardson abruptly ended her tenure with the Brizius, Embry & Smith optometry office, submitting her resignation and departing the practice. However, her departure coincided with administrative checks that immediately raised red flags for the clinic’s leadership.
As management began routine account reconciliations and billing reviews, discrepancies began to surface. Accounts that should have reflected active balances were suddenly showing zeroed-out ledgers, and standard tracking markers for patient histories appeared out of order.
Upon digging deeper into the administrative software, practice owners discovered that a significant volume of financial ledgers had been altered. The edits effectively blocked the clinic from collecting legitimate, outstanding bills from various accounts.
Alarmed by the widespread nature of the data anomalies, clinic leadership escalated the issue, initiating an internal review alongside their designated Information Technology (IT) support team.
The Police Report and Arrest
Recognizing the severity of the data manipulation, the management team formally contacted the Evansville Police Department to file an official fraud report. EPD officers responded directly to the Brizius, Embry & Smith facility to document the complaint, interview staff, and secure initial digital logs.
Initial inquiries by the responding officers revealed that the catalyst for the entire sequence appeared remarkably minor: a personal billing ledger belonging to Richardson herself. The police report noted that Richardson had allegedly deleted her own outstanding balance, which totaled approximately $80.
However, as IT specialists and investigators began extracting system logs and mapping out the scope of the database alterations, the true magnitude of the incident became clear.
What initially looked like a petty attempt by a departing employee to wipe her own slate clean transformed into a sweeping digital tampering investigation. Following the completion of the initial forensic assessment, warrants were issued, leading to Richardson’s formal arrest and booking into the Vanderburgh County Jail on multiple criminal counts.
Supporting Context & Metrics
Breaking Down the Digital Damage
The comprehensive forensic review conducted by the clinic’s IT department and law enforcement investigators unveiled an astonishing volume of compromised data. The alterations were not limited to isolated typographical errors or minor bookkeeping mistakes; they involved sweeping changes across hundreds of files.
According to investigative findings, Richardson’s digital footprint within the system was split into two distinct categories: direct actions taken under her own user profile, and unauthorized actions executed by hijacking a coworker’s digital credentials.
1. Activity Under Richardson’s Personal Credentials:
- Records Impacted: More than 500 individual records across 52 unique patient files.
- Deleted Outstanding Balances: Nearly $15,000 in uncollected patient debts erased.
- Compromised Insurance Adjustments: Nearly $4,000 in legitimate insurance adjustments altered or wiped.
- Erased Patient Payments: Nearly $16,000 in payments already rendered by patients removed from the ledger system.
2. Activity Utilizing Stolen Credentials:
In an escalation of the security breach, investigators discovered that Richardson had allegedly compromised another employee’s authentication credentials to bypass security measures and perform additional database alterations. This secondary wave of tampering compounded the financial and administrative damage:
- Additional Outstanding Bills Deleted: Approximately $10,000 in unpaid balances wiped clean.
- Insurance Adjustments Altered: An additional $3,600 in insurance adjustments modified.
- Prior Patient Payments Erased: Approximately $31,000 in payments that had already been successfully processed and paid by clients wiped from the active ledgers.
The Cumulative Financial and Client Impact
When financial investigators aggregated the total impact of both the direct and credential-hijacked modifications, the figures illustrated a devastating picture for both the business and its clientele.
- Direct Potential Fraud to the Business: Investigators calculated that if the alterations had gone entirely unnoticed and uncorrected, the optometry practice would have suffered a direct financial loss totaling $25,171.34. This sum represents uncollected revenues, wiped insurance adjustments, and vanished payment records that the clinic had a legal and operational right to claim.
- Potential Impact on Innocent Patients: Perhaps even more concerning than the corporate losses was the secondary impact on the clinic’s clientele. Investigators warned that had the database changes not been intercepted and reversed, clients of Brizius, Embry & Smith could have been improperly re-billed for a staggering total of $46,966.16—money they had already paid to the clinic for medical services, glasses, contacts, and examinations.
Such a sweeping wave of erroneous secondary collection notices would have severely damaged patient trust, subjected innocent consumers to unnecessary financial stress, and created a public relations and customer service nightmare for the optometry practice.
Official Statements & Legal Proceedings
The Suspect’s Response and Investigation Interviews
Following her identification as the primary suspect in the digital tampering scheme, Richardson was subjected to formal questioning by law enforcement investigators.
During these interviews, when confronted with the detailed forensic findings, system login logs, and specific database alterations tied to her personnel profile and stolen credentials, Richardson maintained a posture of complete denial.
According to police documentation, Richardson told investigators during questioning that she had "no idea what they were talking about," denying any involvement in the deletion of bills, the alteration of patient records, or the unauthorized use of a coworker’s login credentials.
Despite her denials, the digital trail compiled by the practice’s IT department provided investigators with the electronic evidence necessary to substantiate the criminal charges.
IP addresses, login timestamps, workstation identifiers, and audit trails created an activity log that authorities stated directly linked the alterations to the ten-day window leading up to her departure from the clinic.
Criminal Charges and Legal Exposure
Following the conclusion of the preliminary investigative phase, Richardson was taken into custody and booked into the Vanderburgh County Jail. The scale of the alleged cyber tampering and financial interference resulted in a multi-count criminal indictment filed by prosecutors.
Richardson officially faces the following felony charges:
- Theft: Reflecting the monetary value of services, payments, and balances unlawfully manipulated or diverted from the practice.
- Fraud: Encompassing the deceptive practices utilized to alter financial records and subvert standard business billing operations.
- Modifying Computer Data: A specific charge addressing the unauthorized intrusion, overwriting, and deletion of proprietary electronic files and databases within the practice’s computer system.
Legal experts note that charges related to the unauthorized modification of computer data carry significant penalties, particularly when they involve commercial enterprises, protected health information (PHI), or financial systems where the intended or potential loss exceeds statutory thresholds.
As the case moves through the Vanderburgh County court system, Richardson is presumed innocent until proven guilty in a court of law. However, the state’s evidence—anchored by extensive IT forensics and audit logs—presents a formidable challenge for the defense.
Future Outlook & Industry Implications
Internal Security Reform at Brizius, Embry & Smith
For the Brizius, Embry & Smith optometry office, the incident serves as a harsh lesson in digital security and administrative oversight. Small and medium-sized medical practices—ranging from independent optometry clinics to dental offices and specialized medical practices—frequently rely on small administrative teams where employees enjoy broad access to practice management software.
In the wake of this alleged insider threat, the practice is expected to undergo a comprehensive overhaul of its digital infrastructure. Key remediation steps for the clinic will likely include:
- Role-Based Access Controls (RBAC): Restricting database permissions so that individual employees can only access the specific modules necessary for their daily tasks, preventing front-desk staff from possessing backend ledger-deletion capabilities.
- Credential Management Audits: Mandating strict password policies, eliminating shared logins, implementing Multi-Factor Authentication (MFA), and conducting regular audits of active user accounts.
- Real-Time Monitoring and Anomaly Detection: Installing automated database monitoring tools that flag unusual mass-deletion events, ledger modifications, or off-hours system access immediately rather than waiting for periodic manual audits.
Broader Implications for Healthcare Cybersecurity
Beyond the local impact in Evansville, Indiana, this case highlights a critical blind spot in the broader healthcare cybersecurity landscape. While major hospital networks and large healthcare conglomerates invest heavily in cybersecurity apparatuses, perimeter defenses, and sophisticated Security Information and Event Management (SIEM) systems, smaller private medical practices often operate with minimal IT infrastructure.
Insiders—including disgruntled employees, departing staff members, or individuals facing personal financial distress—frequently possess the physical and digital proximity required to inflict severe damage on corporate databases.
When employees retain administrative privileges after submitting their resignation, the window of vulnerability expands exponentially.
Industry analysts emphasize that medical practices must begin treating internal digital security with the same rigor applied to external cyber threats like ransomware or phishing attacks. By implementing immutable audit logs—records that track every single database query, deletion, and edit in a format that cannot be altered or deleted by standard administrative users—practices can protect both their bottom line and their patients’ sensitive data.
As the legal proceedings against Hannah Richardson advance through the Vanderburgh County court system, the case will undoubtedly be studied by legal professionals, practice managers, and IT security experts alike. It stands as a cautionary tale of how quickly a minor personal debt can escalate into a major felony investigation when digital tools are misused, and why robust internal controls are no longer optional in modern healthcare administration.

0 Comments